Digital forensics & incident response in Austria

When every second counts – we respond immediately.

We guide you through every step of the crisis – calmly, methodically and with the experience of real-world incidents.

24/7available, 365 days a year
≤ 180 minresponse time
3 hrsto on-site deployment
court-admissibleevidence per ISO/IEC 27037
Cyber Trust AustriaOfficially certified
Cyber Trust Austria

No cyber attack announces itself. It strikes – and it strikes hard.

Senior consultants only.

DFIR Austria is the specialist point of contact for companies and organisations in Austria that need fast, competent and discreet support when it matters. As your partner for digital forensics, incident response and IT recovery, we stay with you from the first emergency call until you are fully back to normal operations – with end-to-end services from a single source.

Our team covers the full spectrum: forensic intrusion analysis, structured incident response management, technical system recovery and – where necessary – professional support in ransom situations. We work to the internationally recognised standard ISO/IEC 27037 and make sure that no trace is lost and no decision is taken without a reliable basis.

Incident response

Immediate response to cyber attacks – structured, fast, court-admissible

When ransomware strikes, systems fail or data is compromised, panic does not help – response speed does. DFIR Austria is available around the clock, 365 days a year, and ready to act within a few hours – remotely or on site anywhere in Austria.

Our incident response process starts with immediate triage: we identify the attack vector, stop the spread and, in parallel, secure all relevant digital evidence. From the very first minute we maintain complete chain-of-custody documentation, so that your evidence holds up in court and with insurers.

When it happens

  1. T+00

    Call & triage

    We listen, assess the situation and give you the first instructions straight away.

  2. T+15 min

    Containment

    Identify the attack vector and stop the spread – without destroying evidence.

  3. T+60 min

    Evidence preservation

    Forensic acquisition according to NIST, SANS and ISO/IEC 27037 with a complete chain of custody.

  4. then

    Recovery & report

    Secure recovery, hardening and court-admissible documentation.

No step is taken without coordination – your management is kept up to date in regular situation briefings.

Chain of evidenceSchematic illustration
  1. 01AcquisitiondoneStorage media, memory and logs forensically secured
  2. 02Hash valuedoneSHA-256 calculated at the moment of acquisition
  3. 03LogdoneWho, when, with what – documented without gaps
  4. 04AnalysisrunningOn working copies only – the original remains untouched
  5. 05Expert reportnextCourt-admissible and verifiable by third parties
Original9f2c 4b07 … d3a1 e41aWorking copy9f2c 4b07 … d3a1 e41aHash values identical – evidence unchanged

Emergency card · PDF

The first hour after a ransomware attack

Seven decisions on one A4 page, with our emergency number and space for your own contacts. Print it, put it in your crisis manual, pin it up next to the server room.

Download the emergency cardPDF · A4 · 0.7 MB

Services

Complete DFIR expertise – from a single source

From prevention and the first hour of a security incident to court-admissible documentation for authorities, insurers and courts.

ReconstructionSchematic illustration
  1. Day −14Initial accessMail log
  2. Day −9Admin rightsEvent log
  3. Day −2Data exfiltrationFirewall log
  4. Day 0EncryptionFile system

Undetected in the network: 14 days – visible only by correlating all sources

01 · Digital forensics

Digital forensics at the highest level – evidence that holds up

Digital traces disappear quickly – especially when people act without coordination after an attack. DFIR Austria secures forensic evidence according to scientific standards before any change is made to the systems. Our experts analyse hard drives, memory images, network data, cloud logs and mobile devices – with certified tools and reproducible methods. Our forensic work covers the preservation of evidence from every kind of digital medium – from notebooks, smartphones, servers and databases to backup tapes and vehicles.

The findings are documented in court-admissible expert reports that meet the requirements of Austrian law enforcement, data protection authorities and insurers. Whether internal misuse, an external attack or a data breach – we reconstruct what happened and document it so that you remain able to act.

02 · Detecting threats before they cause damage

Malware analysis & threat hunting

Modern attackers deliberately leave only minimal traces – and often remain undetected in corporate networks for weeks. DFIR Austria combines reactive malware analysis with proactive threat hunting to track down hidden threats before they escalate.

In malware analysis, we examine malicious code both statically and dynamically: we decode persistence mechanisms, reconstruct the attackers’ full radius of action and identify compromised accounts and systems. You receive the results as court-admissible reports in PDF, DOCX and STIX format.

Threat hunting goes one step further: based on current threat intelligence feeds and the MITRE ATT&CK framework, we search your infrastructure specifically for indicators of an ongoing compromise. The result is not just clarity about the current state – but a sound basis for lasting protective measures.

Threat hunt · MITRE ATT&CKSchematic illustration
  • Initial access
  • T1566Phishing
  • T1190Web app exploit
  • T1078Valid accounts
  • Persistence
  • T1053Scheduled tasks
  • T1547Autostart
  • T1136New account
  • Lateral movement
  • T1021Remote services
  • T1570Tool transfer
  • T1550Pass-the-hash
  • Exfiltration
  • T1567Web service
  • T1041Over C2
  • T1048Alt. protocol

2 hits2 under review8 clean

Expert reportSchematic illustration

  1. Mandate & questions of evidence
  2. Findings – secured evidence
  3. Methodology & tools
  4. Analysis
  5. Answers to the questions of evidence
  6. Appendix – hash values & logs

Court-certified and sworn expert witness

03 · Expert reports

Forensic expert reports and analysis of complex cases

Beyond core forensic work, we support you in analysing complex matters in contract law, employment law, competition law and copyright law – right up to preparing for court hearings.

Michael Meixner is a court-certified and sworn expert witness for digital forensics and cyber security. His expert reports are clear and verifiable for courts, authorities and insurers – and they stand up to scrutiny.

04 · Prevention

IT security in Vienna and across Austria – before anything happens

Our expertise ranges from comprehensive security and vendor-independent consulting to penetration testing, management-level audits and cybersecurity assessments.

A cybersecurity assessment examines how well your organisation’s security controls can detect and remediate vulnerabilities. Unlike an audit, which works through a checklist, the risk assessment is aligned with your business objectives – as a basis for targeted measures. In training sessions and workshops, we prepare your team for an emergency.

Maturity levelSchematic illustration
  • Identities & access2 → 4
  • Backup & recovery3 → 5
  • Patch management2 → 4
  • Logging & detection1 → 4
  • Incident plan & exercises1 → 3

Current stateTarget after measuresScale 1–5

All services

Respond, investigate, assess, prevent – all from a single source.

Respond

When it has happened: contain immediately, limit the damage, restore operations.

Assess

Expert reports and case analyses for courts, authorities and insurers.

Prevent

Before anything happens: find vulnerabilities, assess risks, harden systems.

Standards & certification

  • Cyber Trust Austria
  • NIST SP 800-61
  • SANS
  • ISO/IEC 27035
  • ISO/IEC 27037
  • MITRE ATT&CK

Facts & figures

Trust you can measure

20+years of incident experience
2013court-certified and sworn expert witness since 2013
≤ 180minutes to first response – 24/7, 365 days a year
27037ISO/IEC – evidence preservation to court-admissible standards, chain of custody
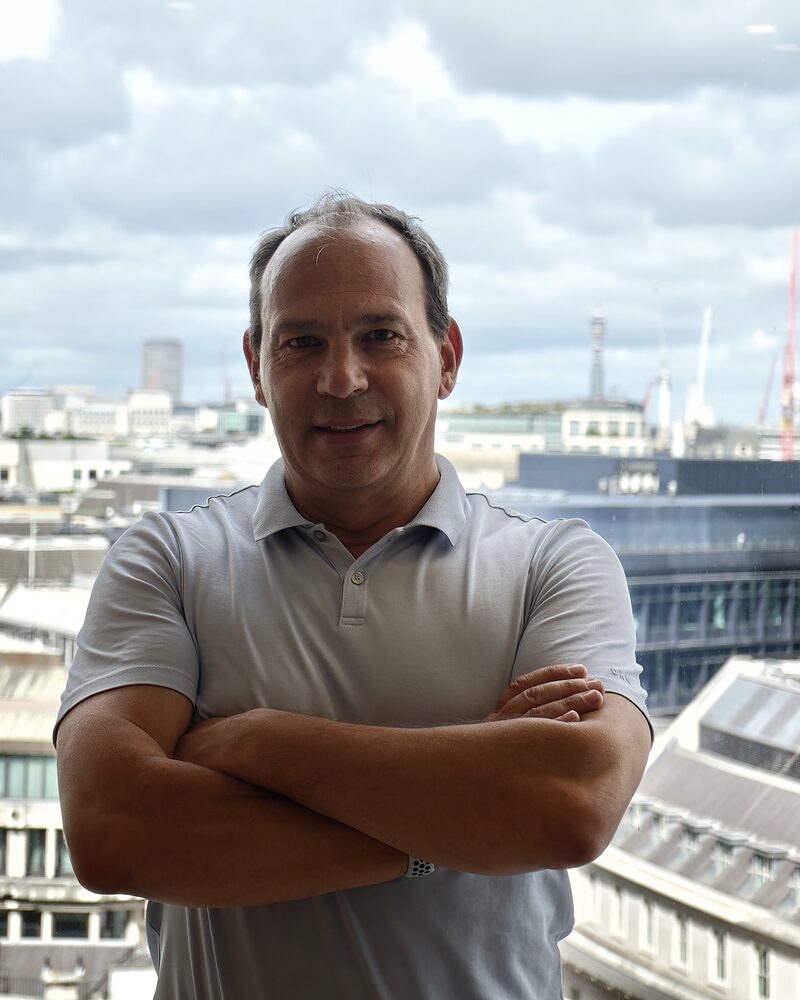
Michael Meixner, founder and managing director of DFIR Austria

Michael Meixner – founder & lead consultant

Senior consultants only

Discretion, experience and a team you can trust

A cyber incident leaves no room for on-the-job training.

That is why our team consists exclusively of experienced senior consultants – experts who know real incidents, work methodically under pressure and know what matters when it counts. Every engagement is led personally by one of our specialists – with direct responsibility, clear communication and the full expertise of the team behind them. No anonymous helpdesk, no passing you on, no starting from scratch.

Our expertise covers the full breadth of a modern attack scenario: from Active Directory and Microsoft 365 to network and endpoint forensics, SIEM, cloud environments and backup systems.

A cyber incident is not just a technical problem – it puts the entire organisation under strain. DFIR Austria understands this and acts accordingly: discreetly, reliably and with the aim of giving you back operational control as quickly as possible. On request, we sign a non-disclosure agreement immediately and communicate only with the contacts you designate.

In addition to the technical analysis, our services include communication with authorities and insurers.

At DFIR Austria, you always speak to someone who knows your case – and has the answers.
Contact

Contact us – before an emergency happens.

In a cyber attack, every minute counts – our team starts the analysis immediately. Whether an acute cyber attack, preventive advice or a forensic expert report: we are available for a free initial consultation.

Emergency 24/7+43 1 226 40 33Emailhello@dfir-austria.at

Businesses – 24/7

  • Free initial assessment of your incident (max. 30 min)
  • Response within 180 minutes
  • Confidential and discreet
  • NDA on request – available immediately

Private clients – daily 09:00–20:00

For matters relating to IT security and digital incidents.