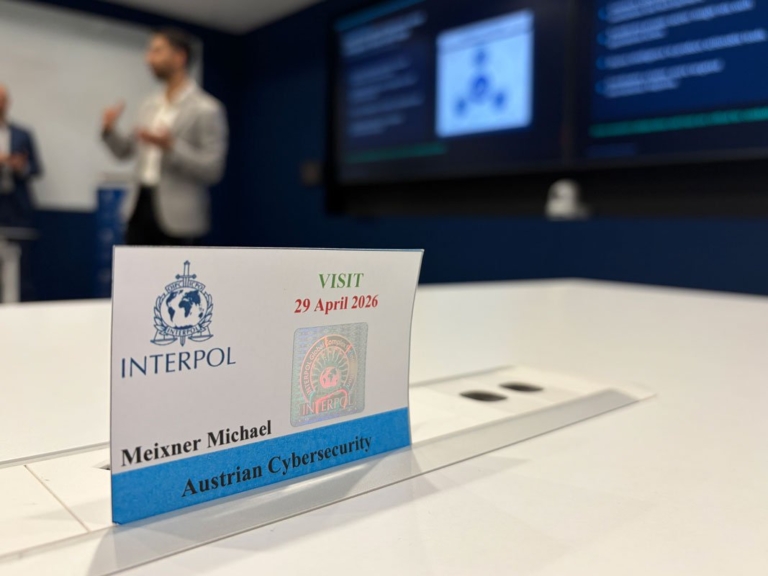
317 hours of professional development – why continuous learning is at the core of my consulting
Certification & expertise · April 2026
As a CISSP-certified IT security professional and sworn expert witness, lifelong learning is not optional for me – it is an obligation. And that obligation pays off directly for my clients.
What is behind the CISSP?
The Certified Information Systems Security Professional (CISSP) is the most widely recognised certification in information security worldwide. Issued by (ISC)², it covers eight domains of knowledge – from security engineering and cryptography to identity & access management. Fewer than 160,000 people worldwide hold this certification. In Austria, the number of active CISSPs is considerably smaller.
Passing the exam once is not enough, however. The CISSP requires continuous professional development – not by accident, but as a deliberate mark of quality.
The CPE requirement: 40 hours a year
Every active CISSP must document at least 120 Continuing Professional Education (CPE) credits in each three-year certification cycle – the equivalent of 40 hours a year. These hours have to be documented, submitted and accepted by (ISC)². Anyone who fails to provide this evidence loses the certification.
CPE hours come from conferences, professional publications, training courses, one’s own talks, webinars or active involvement in the security community – always with a direct link to information security.
- Required in the cycle July 2024 – July 2027: 120 CPE hours
- Actually completed: 317 CPE hours
- Above the requirement: +197 hours
317 hours equal 264 % of the minimum requirement – or almost eight full working weeks that, over the past two years or so, have gone exclusively into professional development.
Why this matters for my clients
The threat landscape is changing rapidly. According to recent figures from the German BSI and ENISA, the number of reported cyber attacks on European companies is rising by 30–40 % a year. Ransomware, supply chain attacks, AI-assisted phishing campaigns, zero-day exploits in widely used business software – what was a niche threat three years ago is everyday business in every security operations centre today.
Anyone advising in this environment cannot rely on yesterday’s knowledge. That is the value of my CPE hours: they are not a bureaucratic box-ticking exercise, but direct proof of quality.
My professional development covers, among other things
- Digital forensics & incident response (DFIR)
- Ransomware tactics & negotiation
- Cloud security & zero-trust architectures
- Cryptocurrency forensics & blockchain analysis
- NIS2, GDPR & regulatory developments
- Threat intelligence & attacker profiling
- Vulnerability management & penetration testing
- Court-admissible documentation & expert witness practice
Vendor-independent – by conviction
My consulting services are deliberately independent of software and hardware vendors. I do not sell products, receive no commissions from manufacturers and do not profit from the sale of particular solutions. That is not a coincidence – it is a principle.
Only someone with no financial incentive to recommend a particular technology can truly act in the client’s interest. My 317 CPE hours span solutions and attack techniques across the entire market – from Microsoft 365 security to open-source SIEM systems, from the forensic analysis of proprietary mobile devices to cloud-native security architectures.
The result: I recommend what fits your organisation – not what pays the best commission.
Professional development protects your organisation
When I identify a vulnerability in your IT infrastructure today, or forensically reconstruct the cause of a security incident, I draw on knowledge that I did not just prove in an exam years ago – but that I have continuously deepened and updated last week, last month and over the past year.
In a discipline where attackers develop new methods every day, current knowledge is not an advantage – it is a prerequisite. More about the team and how we work: about us.